In today’s hyper-connected world, where technology is at the heart of every sector, cybersecurity is more crucial than ever. As the digital landscape evolves, so do the complexities of cyber threats. Amidst this ever-changing environment, a Security Operations Center (SOC) is vital in safeguarding sensitive information and infrastructure from malicious actors. But what exactly is a SOC for cybersecurity, and how does it contribute to protecting organizations from cyberattacks? This article explores the fundamental role of a SOC, its evolution, and why it has become indispensable in modern cybersecurity.
What is a SOC for Cybersecurity?
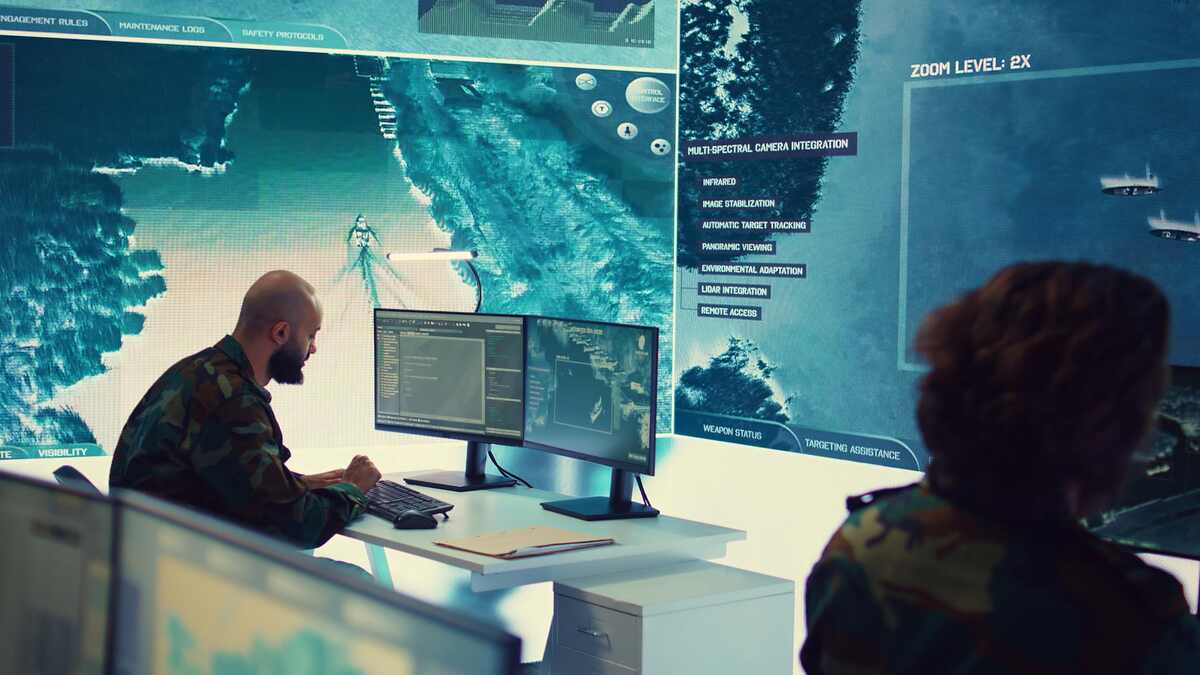
A Security Operations Center (SOC) is a centralized unit that monitors, detects, analyzes, and responds to cybersecurity threats. The SOC is the first line of defense against various cyber threats, including malware, data breaches, and sophisticated attacks like Advanced Persistent Threats (APTs). With the growing sophistication of cybercriminals, a well-established SOC is essential for any organization looking to protect its digital assets.
Key Objectives of a SOC:
- Early Threat Detection: Identifying potential threats early to prevent or mitigate damage.
- Incident Response: Coordinating immediate action during a security breach to contain and neutralize the threat.
- Proactive Threat Hunting: Actively seeking out vulnerabilities and threats before they manifest into full-scale attacks.
- Collaboration: Working with various departments within organization to ensure the comprehensive security of the entire infrastructure.
The Evolution of SOC for Cybersecurity
The rapid advancement of technology has brought about both convenience and risk. Initially, cybersecurity strategies focused on basic perimeter defense and response to incidents. However, as cyber threats evolved, so did the need for more robust and proactive security measures. This evolution gave rise to the SOC—a dedicated unit designed to handle the increasing complexity of cyber threats.
The rise of new attack vectors, including zero-day vulnerabilities, ransomware attacks, and insider threats, has made relying on traditional security methods impossible. The SOC integrates cutting-edge technologies, such as Security Information and Event Management (SIEM) systems, advanced threat intelligence, & machine learning, to stay ahead of evolving threats.
How Does a SOC Function?
A well-functioning SOC operates like a 24/7 command center, with experts constantly monitoring networks, systems, and applications for signs of malicious activity. When a threat is detected, SOC initiates a swift response to contain the breach, analyze the attack’s impact, and prevent further damage.
Core Components of a SOC:
- Real-Time Monitoring: Monitor network traffic, system activity, and user behavior to detect anomalies.
- Incident Response: A structured process of identifying, containing, and mitigating security incidents.
- Threat Intelligence: Leveraging external and internal data to identify emerging threats and vulnerabilities.
- Security Automation: Automating repetitive tasks and threat detection using AI & machine learning to improve efficiency and response times.
SOC Analysts and Cybersecurity Threat Hunting
A SOC’s effectiveness lies not only in its infrastructure but also in its analysts. These experts are crucial in proactively hunting for threats, analyzing potential risks, and preventing breaches before they escalate. Cybersecurity threat hunting involves actively searching for hidden threats that might evade automated systems or go unnoticed by traditional security measures.
SOC analysts act as digital detectives, looking for suspicious activity, data pattern inconsistencies, and network vulnerabilities. They aim to identify hidden threats early and neutralize them before they cause significant damage.
The Importance of SOC for Cybersecurity
The role of a SOC in cybersecurity cannot be overstated. As cyber threats become more sophisticated & frequent, a centralized unit that can quickly detect, analyze, and respond to these threats is paramount. Here are some of the key benefits a SOC offers:
- Improved Security Posture: By continuously monitoring potential threats, a SOC enhances the organization’s ability to detect and respond to attacks swiftly.
- Reduced Risk of Data Breaches: Early detection and rapid response to security incidents minimize the risk of data breaches and financial losses.
- Business Continuity: A SOC ensures that security incidents are handled efficiently, allowing the organization to resume normal operations with minimal disruption.
- Regulatory Compliance: Many industries require businesses to comply with strict data protection and cybersecurity regulations. A well-functioning SOC can help meet these requirements.
Challenges Faced by SOC Teams
Despite their essential role, SOC teams face several challenges in their daily operations. Alert fatigue is one of the most significant hurdles, as analysts are often overwhelmed by a constant influx of alerts, many of which are false positives. Additionally, the rapid pace of evolving threats means that SOC analysts must constantly update their skills to stay ahead of cybercriminals.
- Skill Gaps: As cyber threats become more advanced, the demand for highly skilled SOC analysts has outpaced supply, leading to skill gaps that can hinder an organization’s ability to respond effectively.
- Resource Limitations: With growing cyber threats, SOC teams often face pressure to do more with fewer resources, which can lead to burnout or inefficiency.
Key Skills for SOC Analysts
To effectively defend against modern cyber threats, SOC analysts must possess technical expertise and soft skills. Some of the key skills required include:
- Technical Expertise:
- Proficiency in intrusion detection and prevention systems.
- Experience with SIEM tools and security automation.
- Understanding of network traffic analysis and system forensics.
- Soft Skills:
- Strong communication skills for coordinating with many departments.
- Problem-solving abilities for responding to security incidents.
- Attention to detail and critical thinking.
The Future of SOC for Cybersecurity
The future of SOCs will be shaped by technological advancements, including artificial intelligence (AI), automation, and quantum computing. These technologies are expected to enhance the capabilities of SOCs by improving threat detection accuracy, automating routine tasks, and reducing human error.
Moreover, as Internet of Things (IoT) expands, SOCs must adapt to the increasing volume of devices connected to the network, each representing a potential entry point for cyberattacks. Integrating AI and machine learning will allow SOCs to scale efficiently and keep up with the growing complexity of cybersecurity threats.
Conclusion
A Security Operations Center (SOC) is the cornerstone of any organization’s cybersecurity strategy. As cyber threats become more sophisticated & pervasive, SOCs provide the critical infrastructure to protect sensitive data and systems. From real-time monitoring to incident response and threat hunting, the role of a SOC is multifaceted and vital in maintaining a robust defense against cyberattacks.
By understanding the importance of a SOC and its key components, organizations can better prepare to face the ever-evolving landscape of cybersecurity risks. As technology advances, SOCs will play an even more integral role in ensuring the safety and security of digital infrastructures worldwide.