In today’s digital age, cyber threats are evolving faster than ever. Organizations across all sectors need a proactive approach to security, and that’s where a SOC analyst steps in. Acting as the first line of defence, this cybersecurity role is vital in detecting, analyzing, and responding to real-time security incidents that could otherwise devastate digital infrastructure.
Core Role of a SOC Analyst
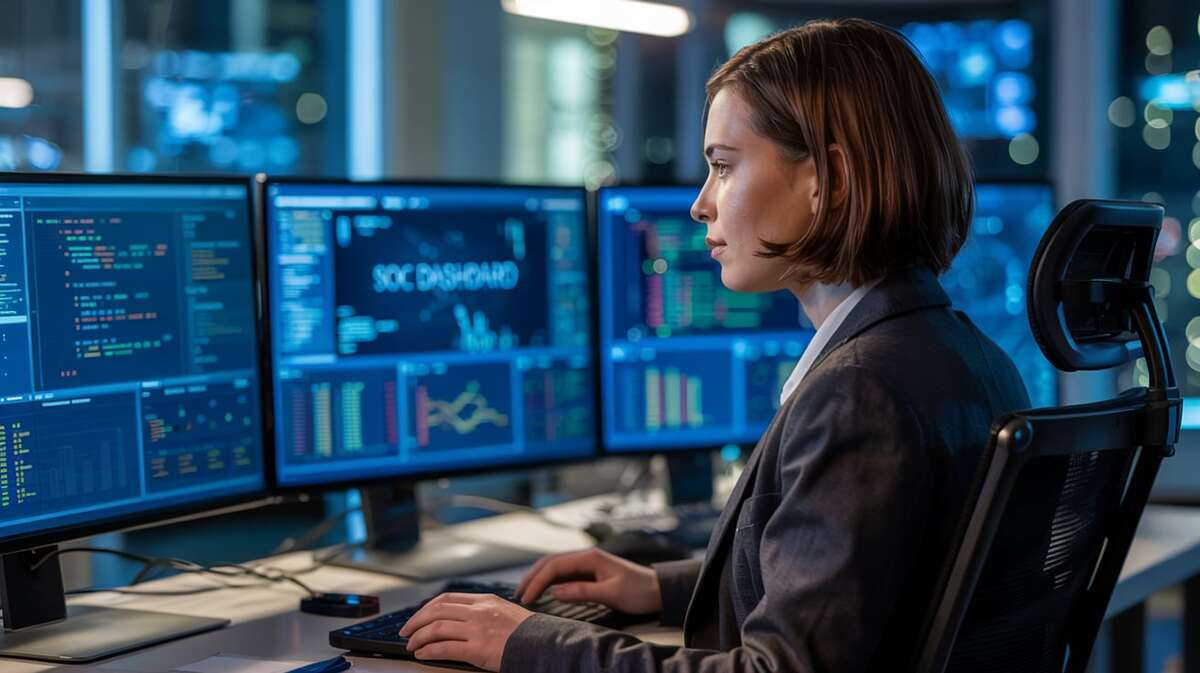
A SOC (Security Operations Center) analyst is responsible for safeguarding an organization’s digital assets by identifying and mitigating security threats. They work within a centralized team that monitors networks, systems, and devices 24/7 for signs of malicious activity.
This role is not just about reacting—it’s about preventing. From filtering false positives to responding to actual breaches, the analyst ensures the organization remains resilient in the face of growing cyberattacks.
Key Responsibilities
The scope of a SOC analyst’s responsibilities is broad and intensive, including:
- Monitoring & Alerting
- Constant surveillance of networks using advanced SIEM tools like Splunk, IBM QRadar, and ArcSight to detect anomalies and unauthorized access.
- Incident Response & Triage
- nvestigating alerts, identifying false positives, escalating real threats, and initiating response protocols such as containment or isolation.
- Vulnerability Assessment
- Scanning systems to uncover weaknesses, then working with teams to patch or mitigate those flaws.
- Threat Intelligence Integration
- Using external data sources and real-time feeds to stay ahead of new and evolving threats.
- Documentation & Reporting
- Creating logs and incident reports for compliance, forensics, and decision-making purposes.
Essential Skills and Qualifications
To thrive as a SOC analyst, professionals need a well-rounded technical and analytical foundation:
- Technical Acumen
- Deep understanding of TCP/IP, firewalls, IDS/IPS systems, and operating systems (primarily Linux and Windows).
- SIEM Expertise
- Experience using security information & event management (SIEM tools) to interpret large volumes of security data.
- Critical Thinking
- The ability to identify patterns in complex environments and recognize when something is “off.”
- Communication Skills
- Conveying threat reports and incident summaries clearly to both technical teams and executives.
Career Entry Points and Growth
The field offers ample opportunity for growth, especially for those starting as an entry-level SOC analyst. Many cybersecurity professionals begin here before moving into roles like:
- Threat Hunter
- Security Engineer
- Penetration Tester
- Cybersecurity Analyst
- ncident Responder
Entry-Level SOC Analyst Path
To start, most professionals pursue a combination of education and certifications, such as:
- CompTIA Security+
- Certified SOC Analyst (CSA)
- Cisco CyberOps Associate
Some employers also look for a degree in computer science, cybersecurity, or a related discipline, but real-world lab experience and internships can be equally important.
SOC Analyst Salary Expectations
Compensation in this field is highly competitive. The average SOC analyst salary ranges between $65,000 and $115,000 annually, depending on experience, certifications, and organizational size. Entry-level positions often start at lower end, with room for rapid growth based on performance.
Standard Tools Used by SOC Analysts
To maintain visibility and control, SOC teams leverage a wide set of tools, including:
- SIEM Solutions (Splunk, QRadar, LogRhythm)
- Endpoint Detection & Response (EDR) tools (CrowdStrike, Carbon Black)
- Packet Analysis Tools (Wireshark, tcpdump)
- Threat Intelligence Platforms (Recorded Future, MISP)
Why Organizations Need SOC Analysts
As threat actors become more sophisticated—leveraging ransomware, phishing, and zero-day vulnerabilities—having an SOC analyst on duty is no longer optional. They manage ongoing threats and help ensure compliance with data protection laws and industry regulations.
Final Thoughts
The role of a SOC analyst is both challenging and rewarding. It demands vigilance, technical sharpness, and continuous learning. For individuals passionate about cybersecurity, it’s a high-impact career that offers stability, prestige, and upward mobility.